
Compliance that matches the system
A privacy notice describes one state of affairs; the system is usually in another. The gap opens quietly, and it is found during an audit.
Built in, not bolted on
Four things that are part of how the platform works, not settings someone has to remember to turn on.
Documents generated from configuration
The privacy notice and cookie policy are produced from the service catalogue actually configured in the system, together with a consent management interface. When the configuration changes, so does the document.
Data residency
All data in a data centre in Budapest, on hardware we own and operate. Hungarian jurisdiction, no onward transfers, and no third-party processor that isn't named in your documentation. Backups stay in a second Hungarian data centre.
Field-level access control
Exposure is controlled down to individual fields, so sensitive data can be present in the system without being visible to everyone who can open the record.
No silent third parties
No plugins calling home, no external scripts collecting quietly, and no third-party verification service on your forms.
Access control
Every user sees exactly what they're permitted to see — nothing more. Permissions are defined at the role and functionality level: who can create, edit, publish or delete, and within which modules. The platform uses a policy-based permission system that maps to how organisations actually work: by role and responsibility, not by individual field configuration.
Form data management
Forms are where personal data enters your system, which makes them the most compliance-critical part of any content platform. The platform treats form data accordingly.
Automatic data expiry
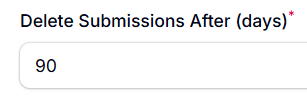
Every form can be configured to purge its collected data automatically after a defined number of days — calculated from the form's expiry date. Once a form is no longer active, the clock starts. No manual cleanup, no forgotten datasets sitting in a database years after an event.
Sensitive field handling
Each form field can be individually marked as containing sensitive data. Marked fields are masked in the interface — visible only to authorised data owners, hidden from everyone else. Email addresses are masked by default, without any additional configuration required.
Data ownership
Forms can be assigned dedicated data owners — the only users who can export submissions or import pre-existing lists. Exports are password-protected, non-editable Excel files: the data owner sets the password at the time of download, and only they can open the file.
Follower notifications
Users can follow a form to receive notifications about new submissions or aggregate counts — without ever seeing the underlying data. Followers know that responses are coming in. The data itself remains invisible to them.
Agents under identity, not around it
Agents in the platform operate under a user. Not alongside one, not through a service account: permissions are attached to an identity, and an agent cannot act without one.
Every action an agent takes is therefore attributable the same way a person's is — same permissions, same audit trail, same answer to “who did this, and when”.
Every exchange on the record
AI communication passes through a gate. Every prompt sent and every response received is retained in the system, together with the token usage behind it.
This means the question a procurement review will ask — what left our system, and when — has an answer that doesn't depend on a supplier's assurance. It is in the same audit record as everything else.
The audit answer
Every change is attributable: who, when, from which address, and what exactly changed, field by field, with previous and new values. Retention is configurable per content type — keep everything, or clean automatically after a defined period.
When a supervisory authority or an internal auditor asks what a page said six months ago, or who removed a consent record, the answer is in the system rather than in a reconstruction.
What we don't claim
We don't hold a certification, and this page isn't legal advice. What the platform provides is the technical basis for compliance — data residency, access control, auditability, retention and consent — with the relevant regulatory requirements in view.
Whether your specific processing is lawful is a question for your data protection officer, not for a supplier's website.
Access control is policy-based, covering every model and operation — create, read, update, delete — enforced at the framework level. The admin interface automatically respects these policies: users only see what they are authorized to access. Roles and permissions are built on Spatie Permission with 24-hour caching; changes take effect without a deployment.
Each form can be configured with an expiry date. Once the form is no longer active, the system automatically begins counting down to the deletion date and purges collected data after the defined number of days. No manual cleanup, no forgotten datasets persisting years after an event.
Any individual form field can be marked as containing sensitive data, regardless of field type. Marked fields are masked in the interface and visible only to authorized data owners. Email address fields are masked by default without any additional configuration.
Any authorized user can be designated as a data owner for a specific form. Data owners are the only users permitted to export submissions or import pre-existing lists. Assignment is done per form in the admin interface.
When a data owner exports form submissions, they set a password at the time of download. The exported file is a non-editable Excel file, encrypted with that password. Only the person who set the password can open it — no one else in the system has access to the export after it leaves.
Yes. Every model change is automatically tracked — who made it, when, from which IP address, and what exactly changed, field by field, with old and new values. Login and logout events are recorded with IP and user agent. Audit logs are automatically pruned after 365 days (configurable).
All data is stored in European data centers. No transfers to third-party servers abroad. No plugins phoning home, no external scripts with hidden data collection.